Open-Vsx

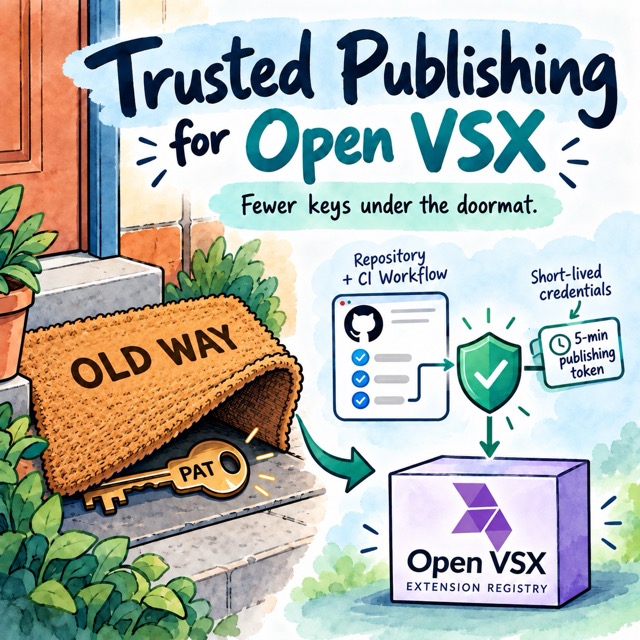
Fewer keys under the doormat: why trusted publishing matters for Open VSX

Fewer keys under the doormat: why trusted publishing matters for Open VSX

Mikaël Barbero

Every software registry eventually learns the same lesson: the most valuable thing in a publishing pipeline is not the code. It is the credential that lets someone ship it.

For most of its history, publishing an extension to the Open VSX Registry from CI has meant creating a personal access token and storing it as a secret in a pipeline. That token is a key left under the doormat. It works at any time, from anywhere, for whoever finds it, and it keeps working until someone notices it should not.

Trusted publishing is now available on Open VSX. Tamas Cservenak has already written a practical guide to setting it up. This post is about something else: why we think it matters, which threats it addresses, which ones it deliberately leaves to other controls, and where it fits in the way we approach the security of the registry.

Open VSX security update, October 2025

Open VSX security update, October 2025

Mikaël Barbero

Over the past few weeks, the Open VSX team and the Eclipse Foundation have been responding to reports of leaked tokens and related malicious activity involving certain extensions hosted on the Open VSX Registry. We want to share a clear summary of what happened, what actions we’ve taken, and what improvements we’re implementing to strengthen the security of the ecosystem.

Vulnerability in Eclipse Open VSX Registry extension publication process

Vulnerability in Eclipse Open VSX Registry extension publication process

Mikaël Barbero

On May 4th, the Eclipse Foundation (EF) Security Team received a notification from researchers at Koi Security regarding a potential issue in the Eclipse Open VSX marketplace extension publication process. The EF Security Team immediately contacted the Eclipse Open VSX team, and upon confirming the issue, work on a fix was promptly initiated.